CVE-2024-26152 Details
Description
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 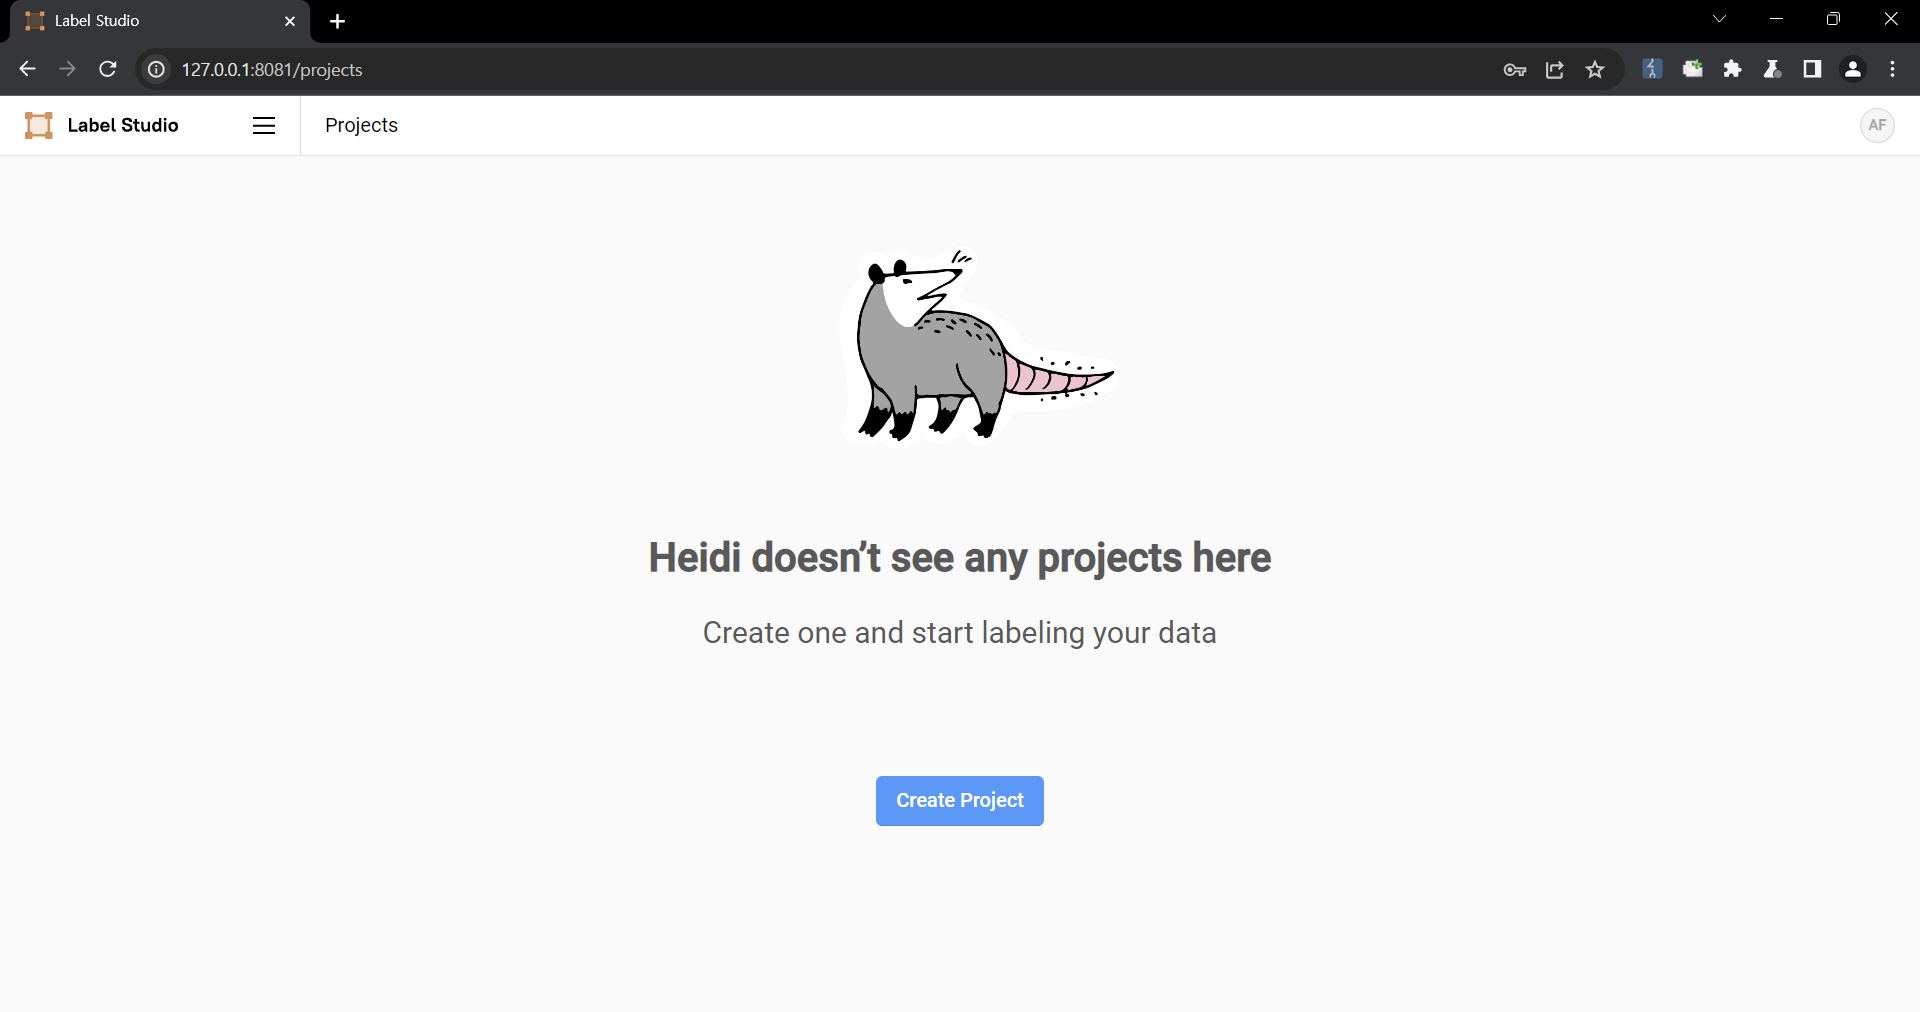 2. Upload a file containing the payload using the "Upload Files" function. 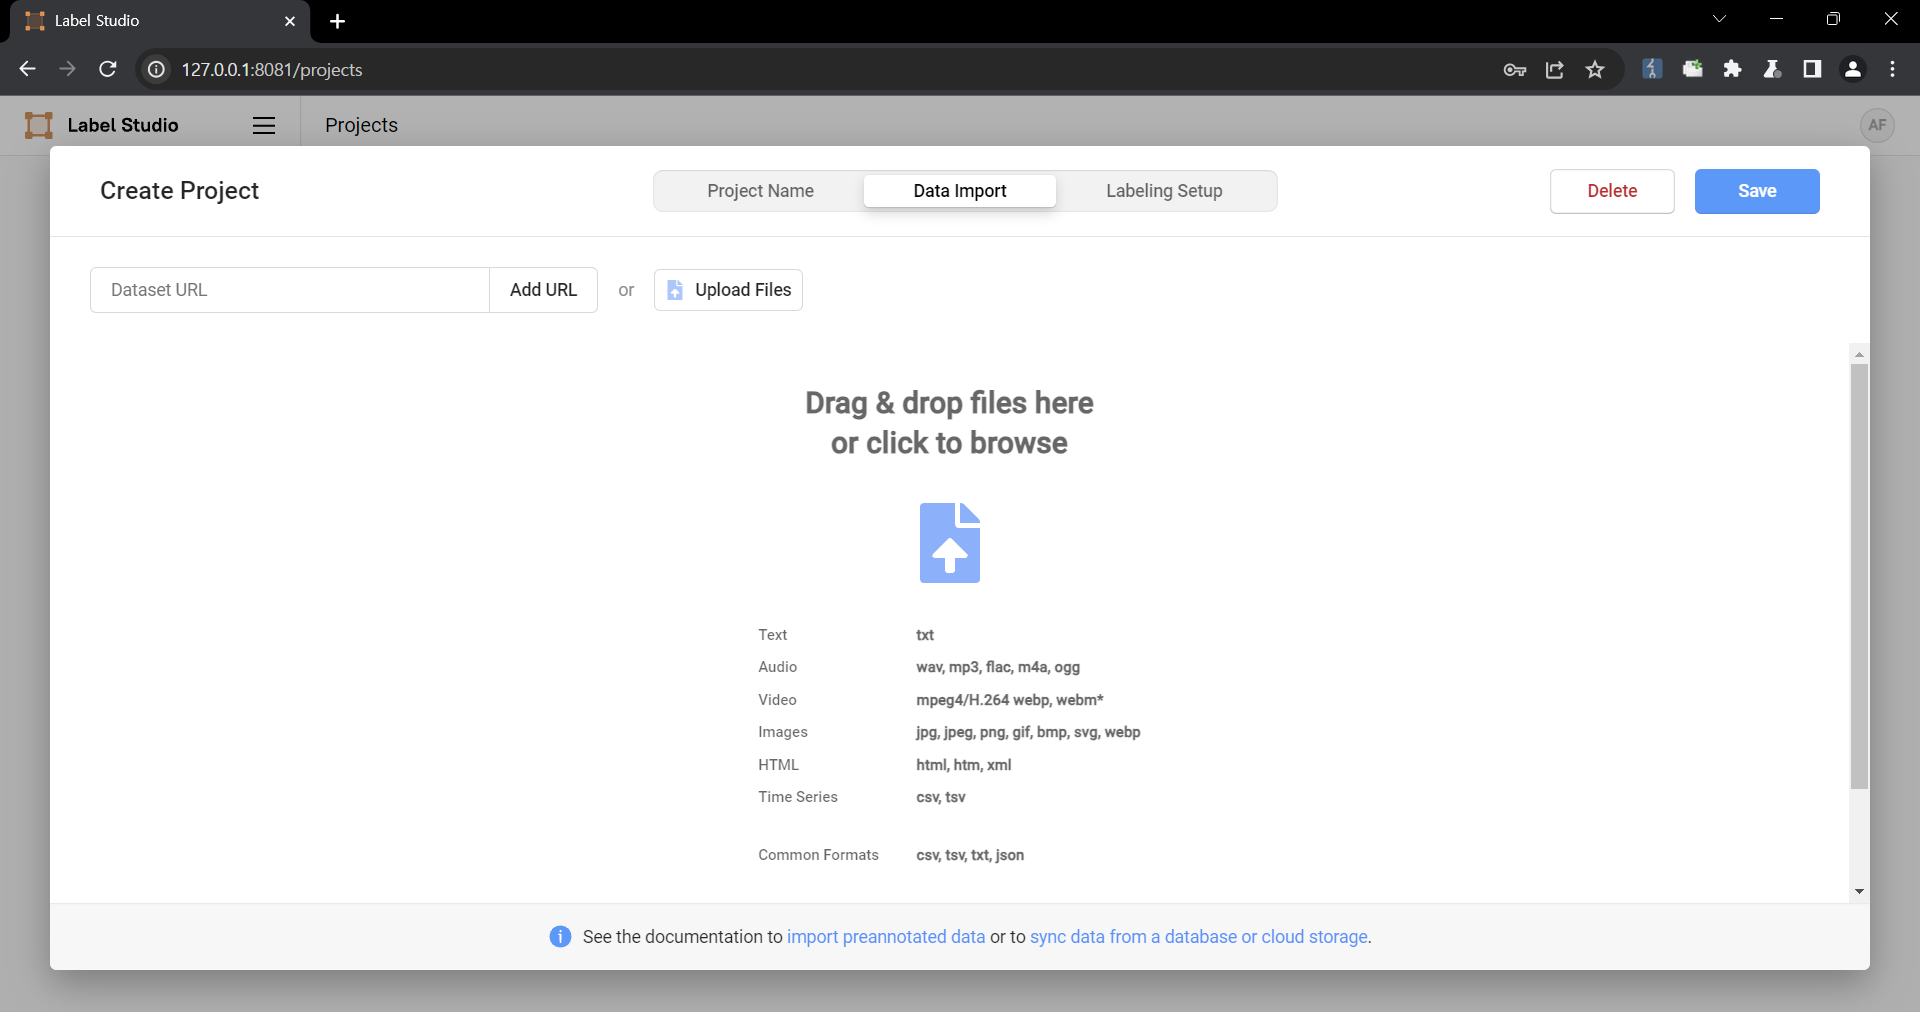 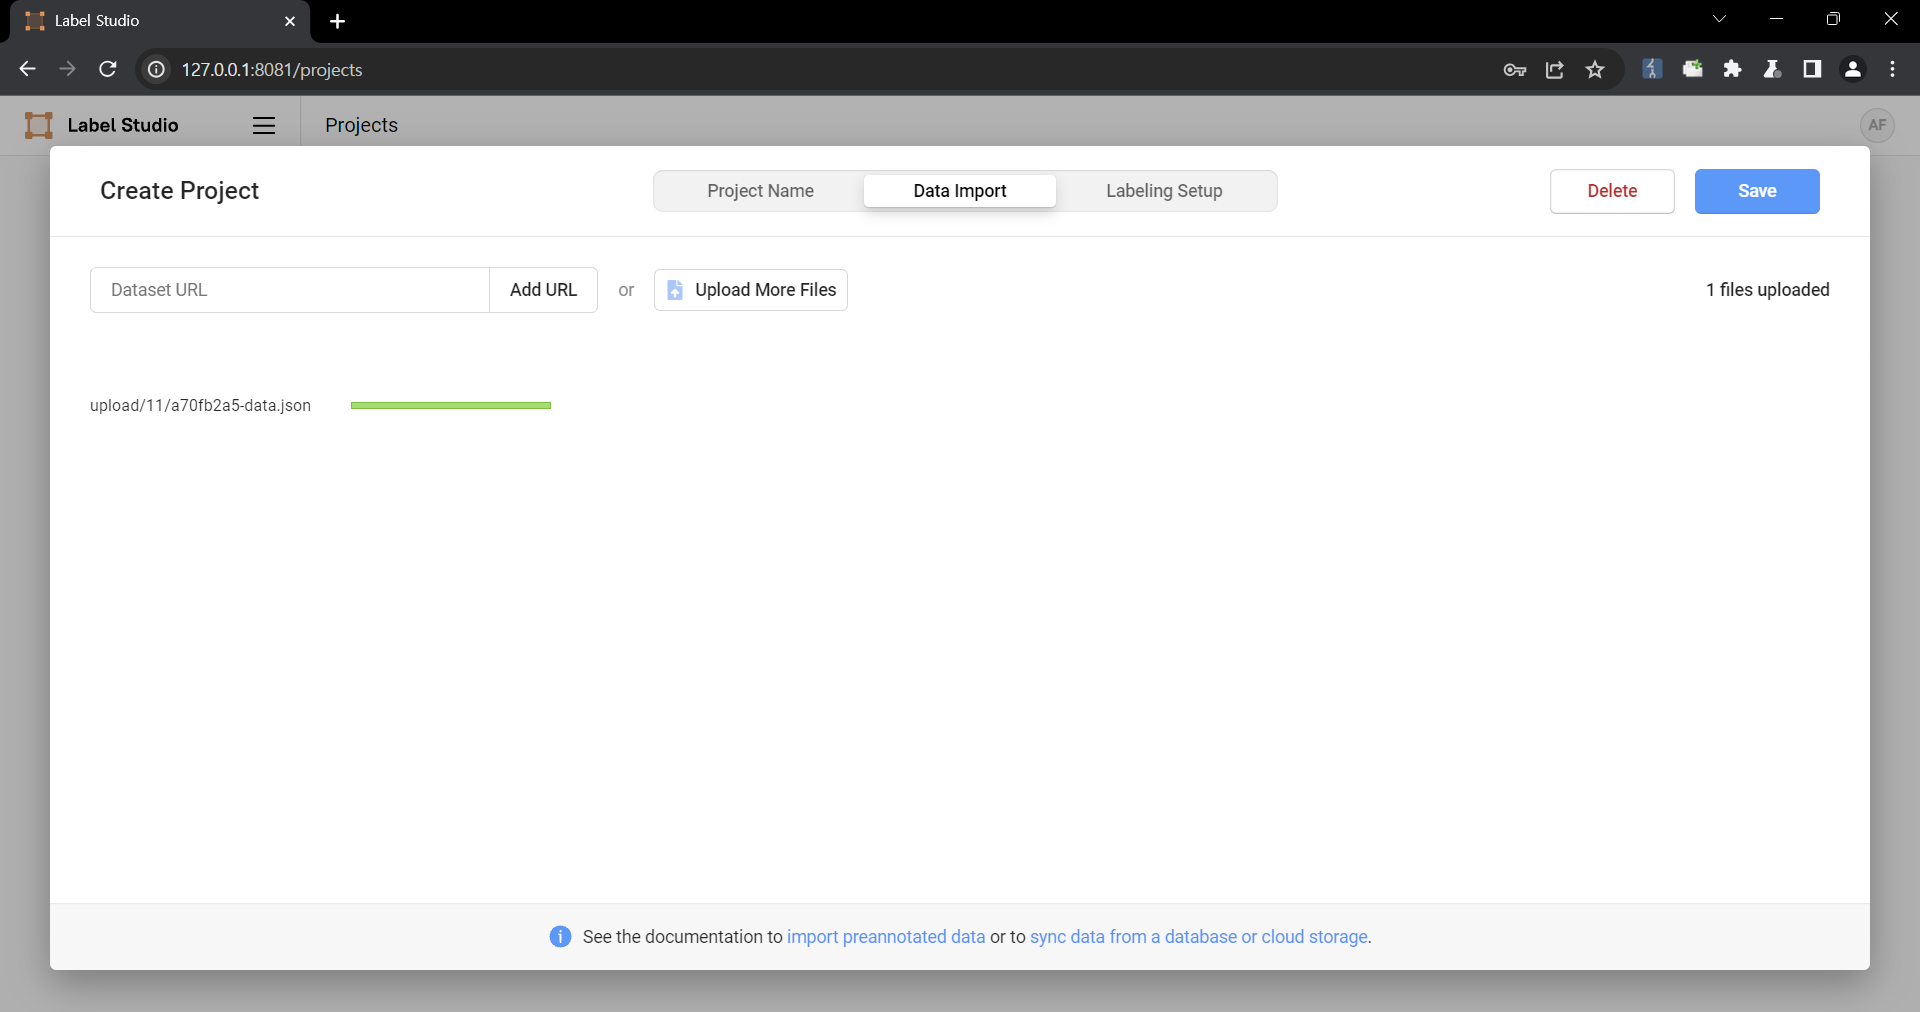 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring 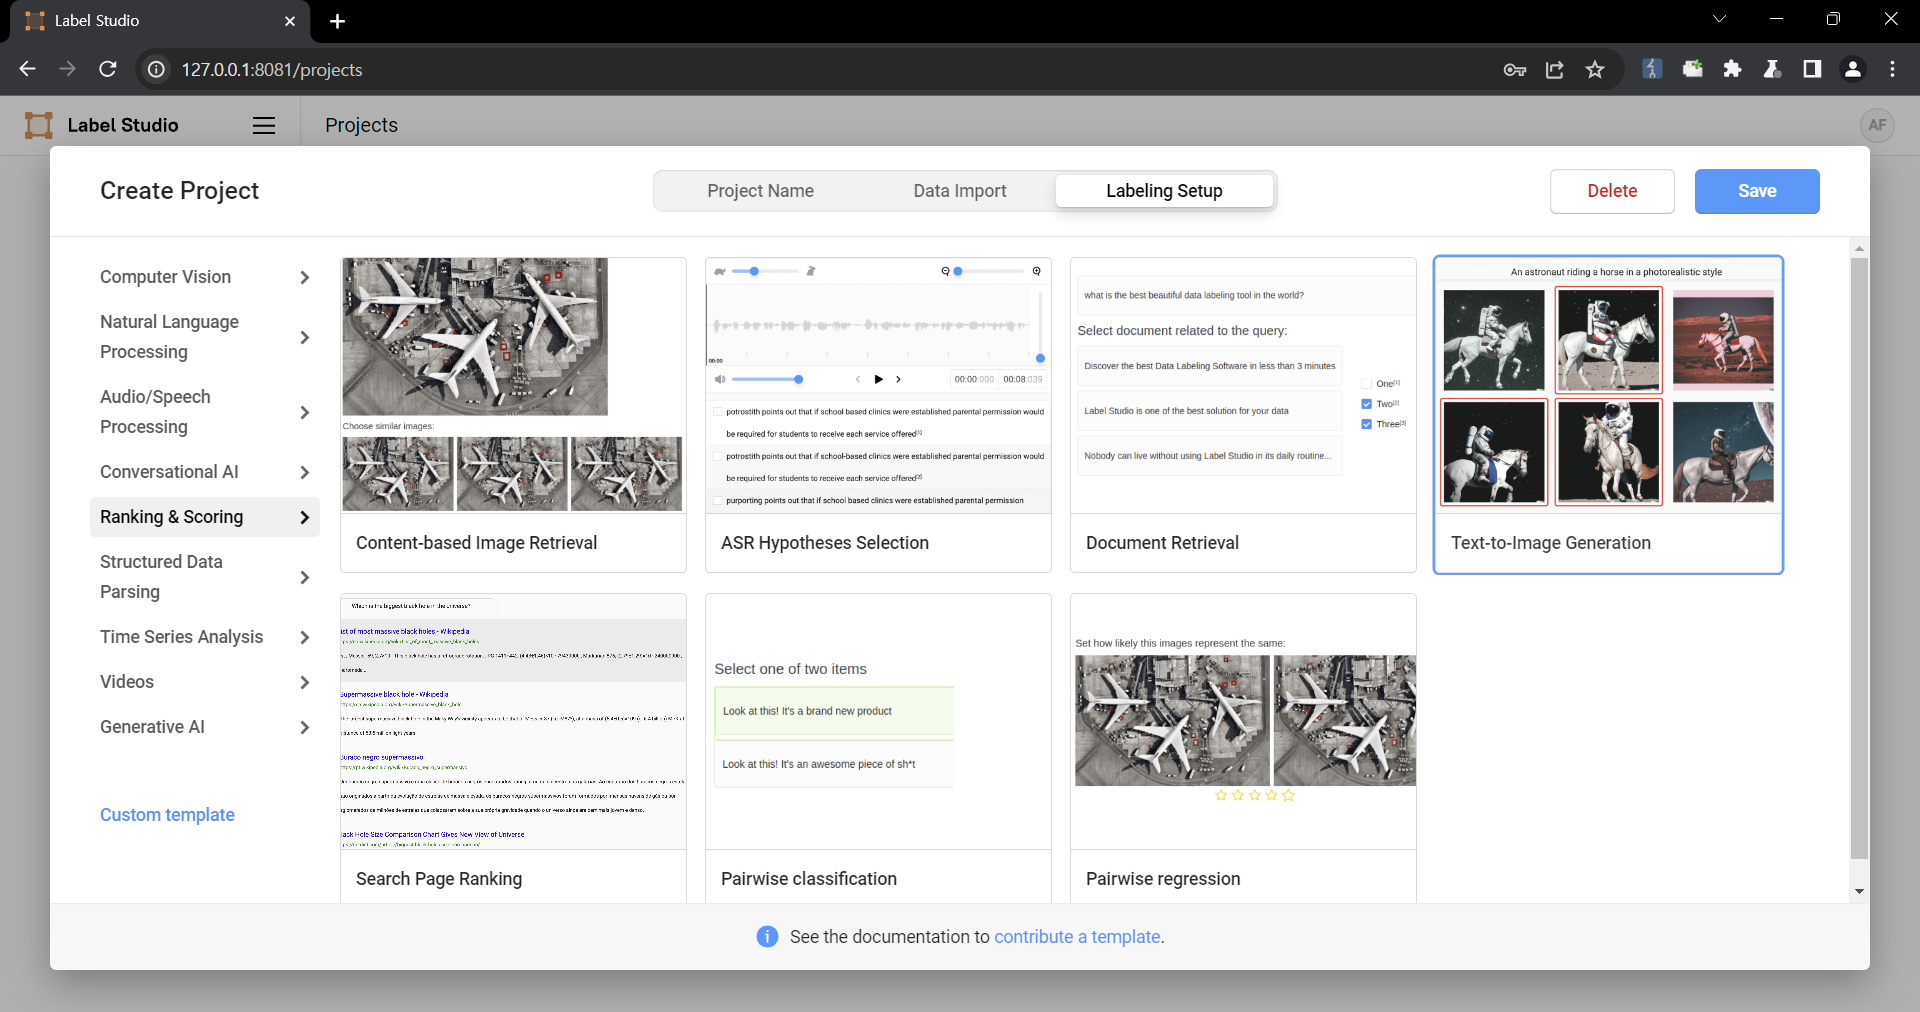 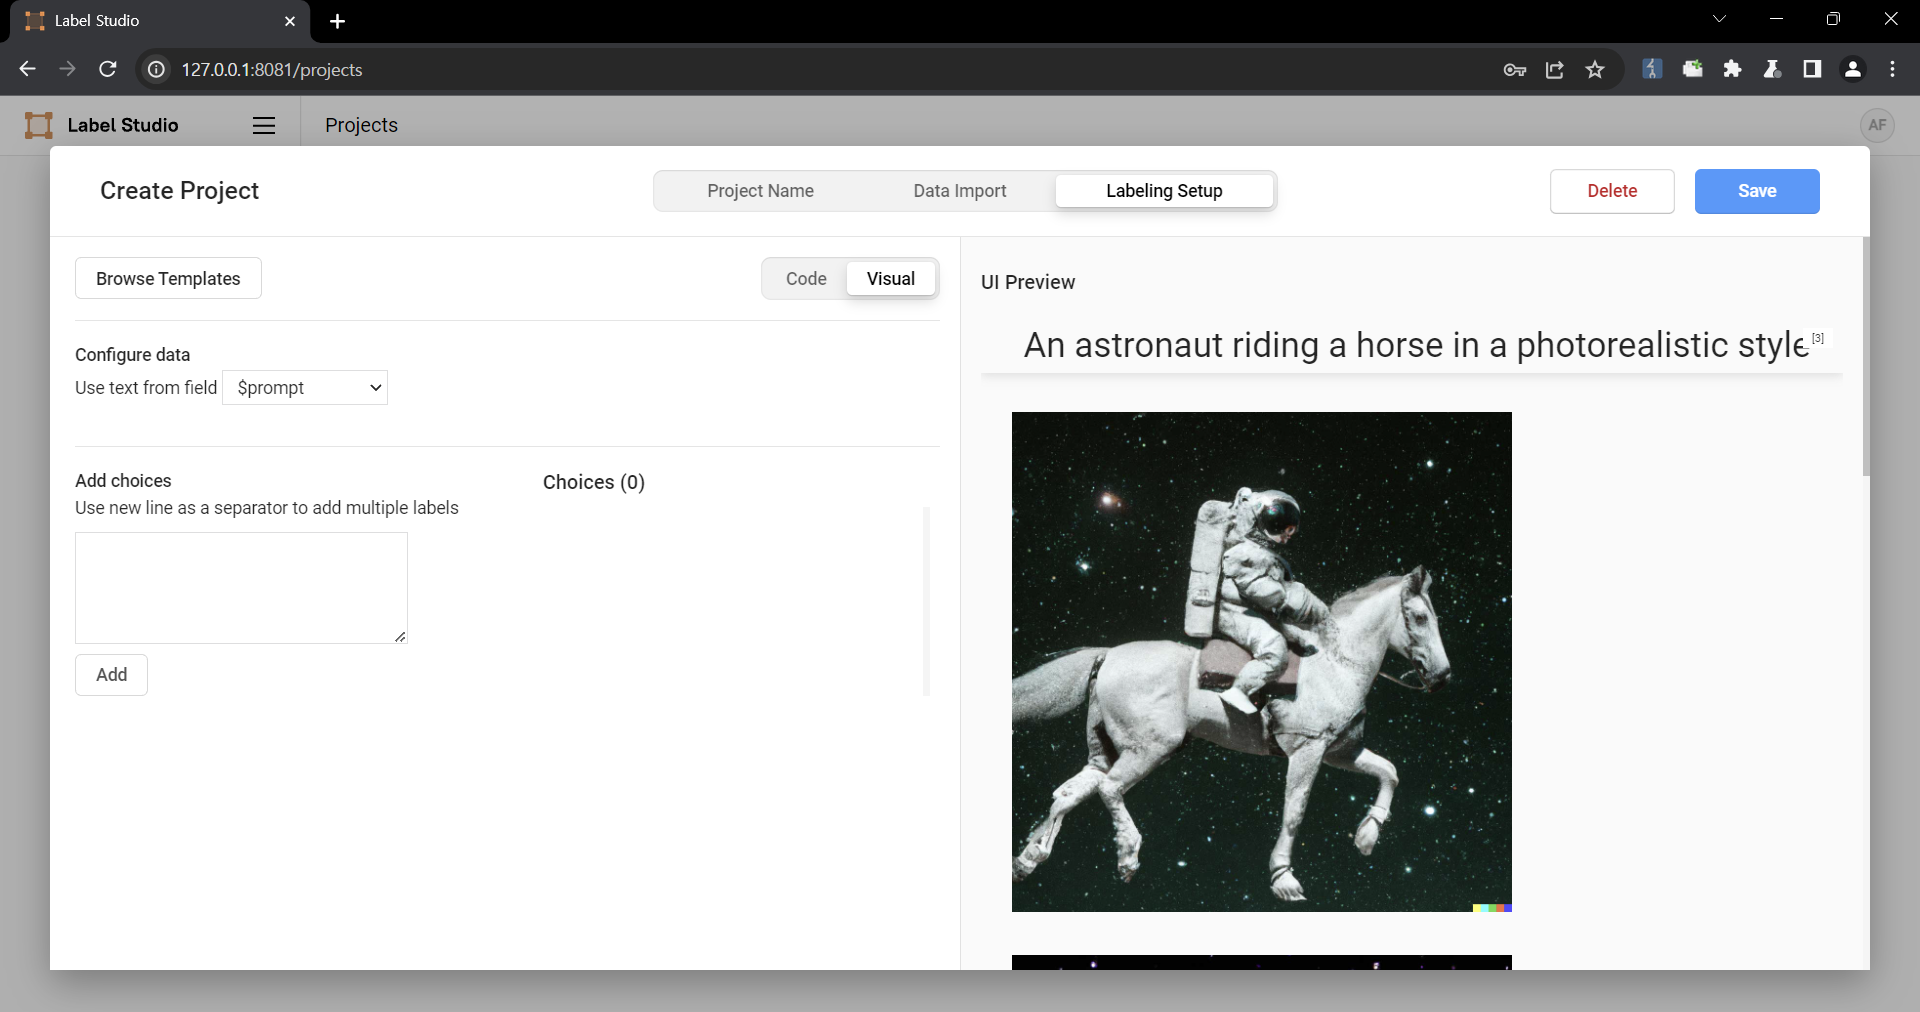 4. Select a task 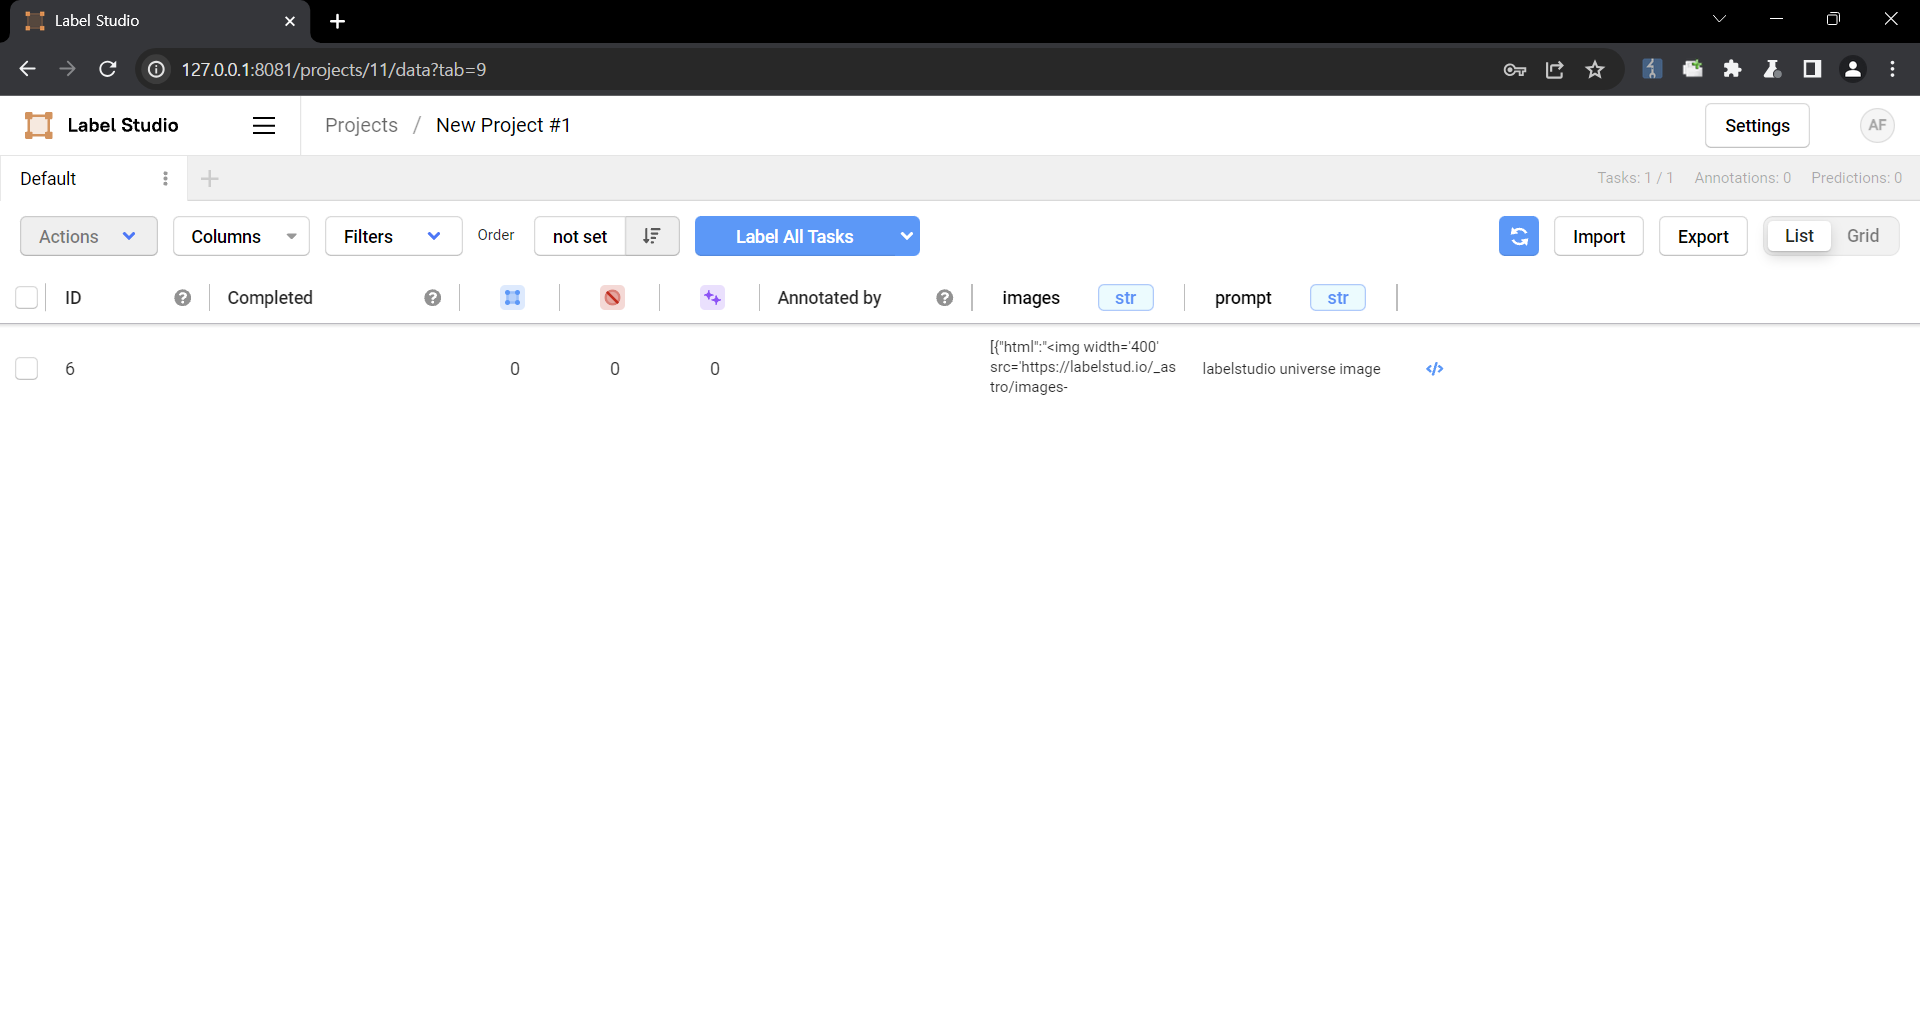 5. Check that the script is running 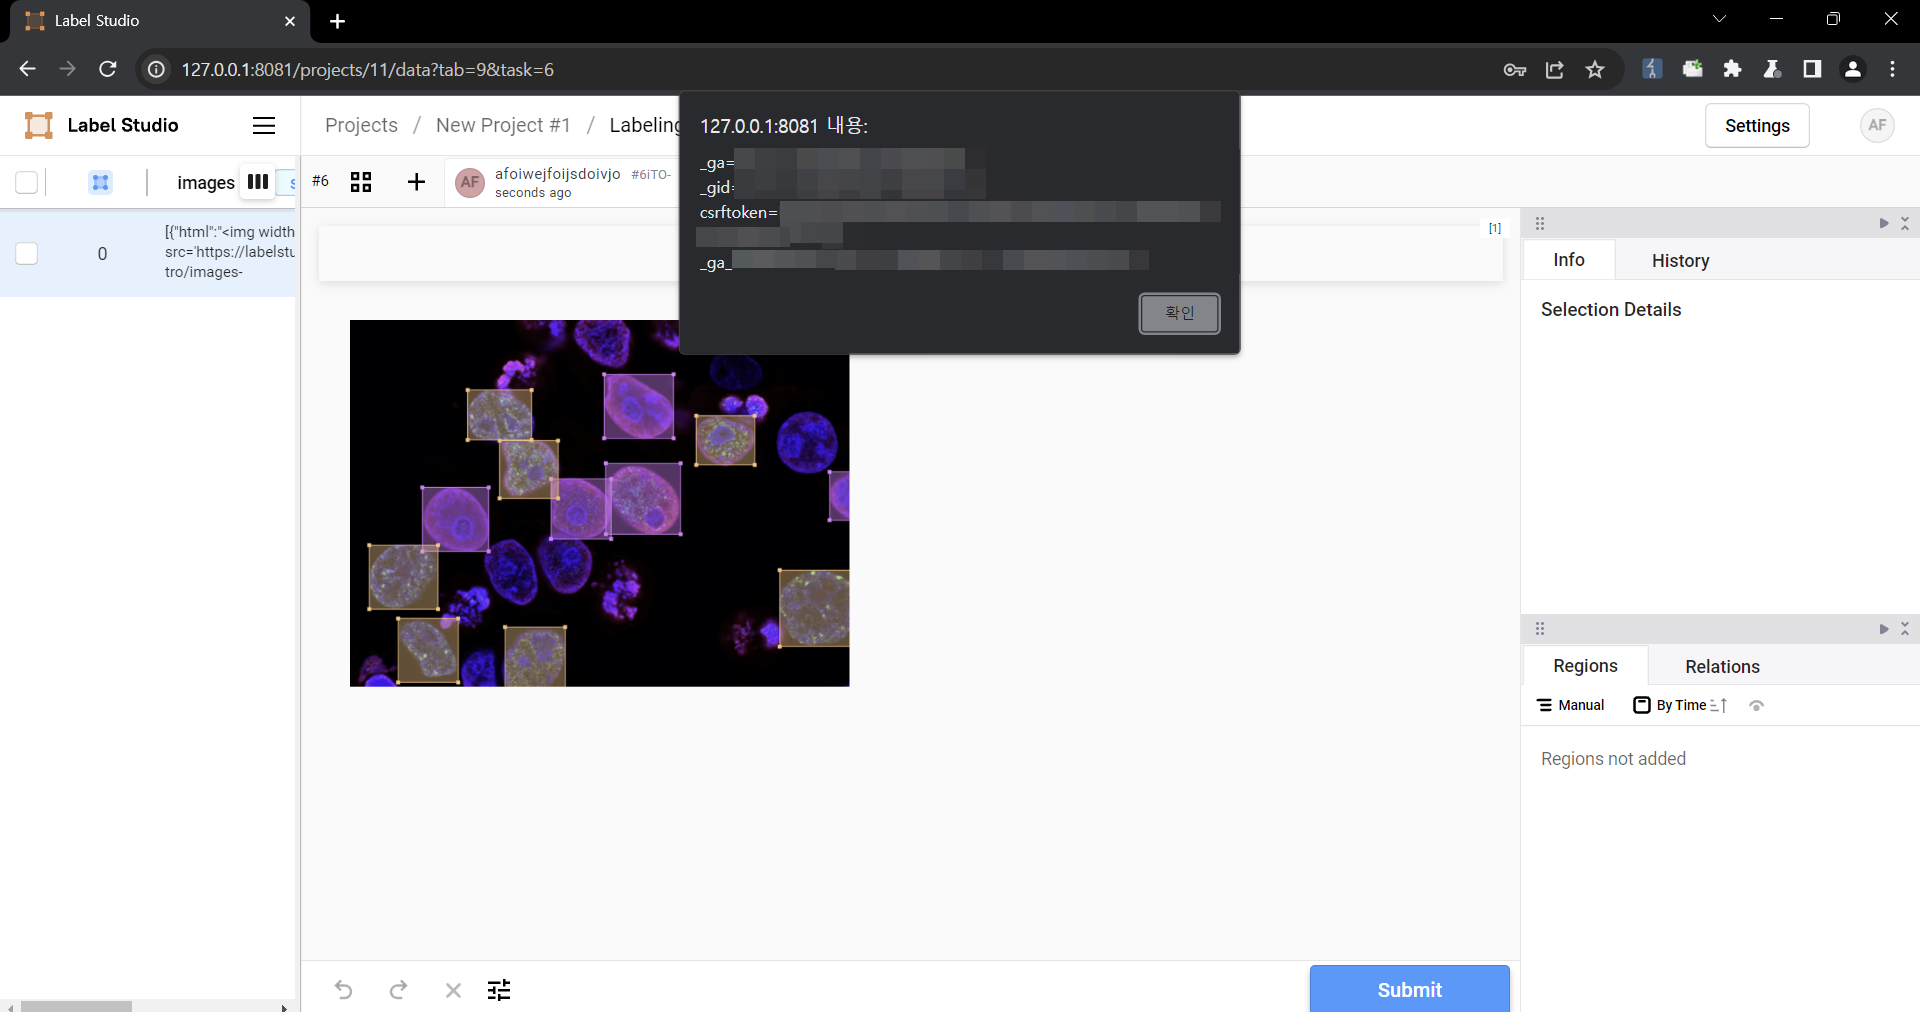 ### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
Metrics
CVSS 4.0 Severity and Vector Strings:
No CVSS 4.0 data is available for this CVE.
CVSS 3.x Severity and Vector Strings:
No data available for CVSS Version 2.0 on this CVE.
CISA-ADP
Assessed Feb 23, 2024References to Advisories, Solutions, and Tools
By selecting these links, you will be leaving this site. These are references gathered from the official CVE record and are not endorsed by Volerion.
Weakness Enumeration
| CWE-ID | CWE Name | Source |
|---|---|---|
| CWE-79 | Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') | [email protected] |
| CWE-79 | Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') | [email protected] |
Affected Products
| Product | Versions |
|---|---|
| humansignal label studio | < 1.11.0 |
CPE
Remediation
| |
Change History
6 change records found show changes
| Date | Action | Recorded By |
|---|---|---|
| Jun 17, 2026 | CVE Modified | [email protected] |
| Jun 17, 2026 | CVE Modified | CISA-ADP |
| May 16, 2025 | Initial Analysis | [email protected] |
| Nov 21, 2024 | CVE Modified | CVE |
| May 14, 2024 | CVE Modified | [email protected] |
| Feb 22, 2024 | New CVE Received | [email protected] |